Resources
See how your workloads communicate and cloud identities behave.
Know when either changes.
CloudFence turns your own cloud logs into behavioral baselines, revealing behavior changes that static rules and posture checks miss -without agents, firewall VMs or traffic redirection.

Outbound Traffic Control
WHAT WE UNCOVER
AI workloads were connecting to destinations the security team wasn't aware of
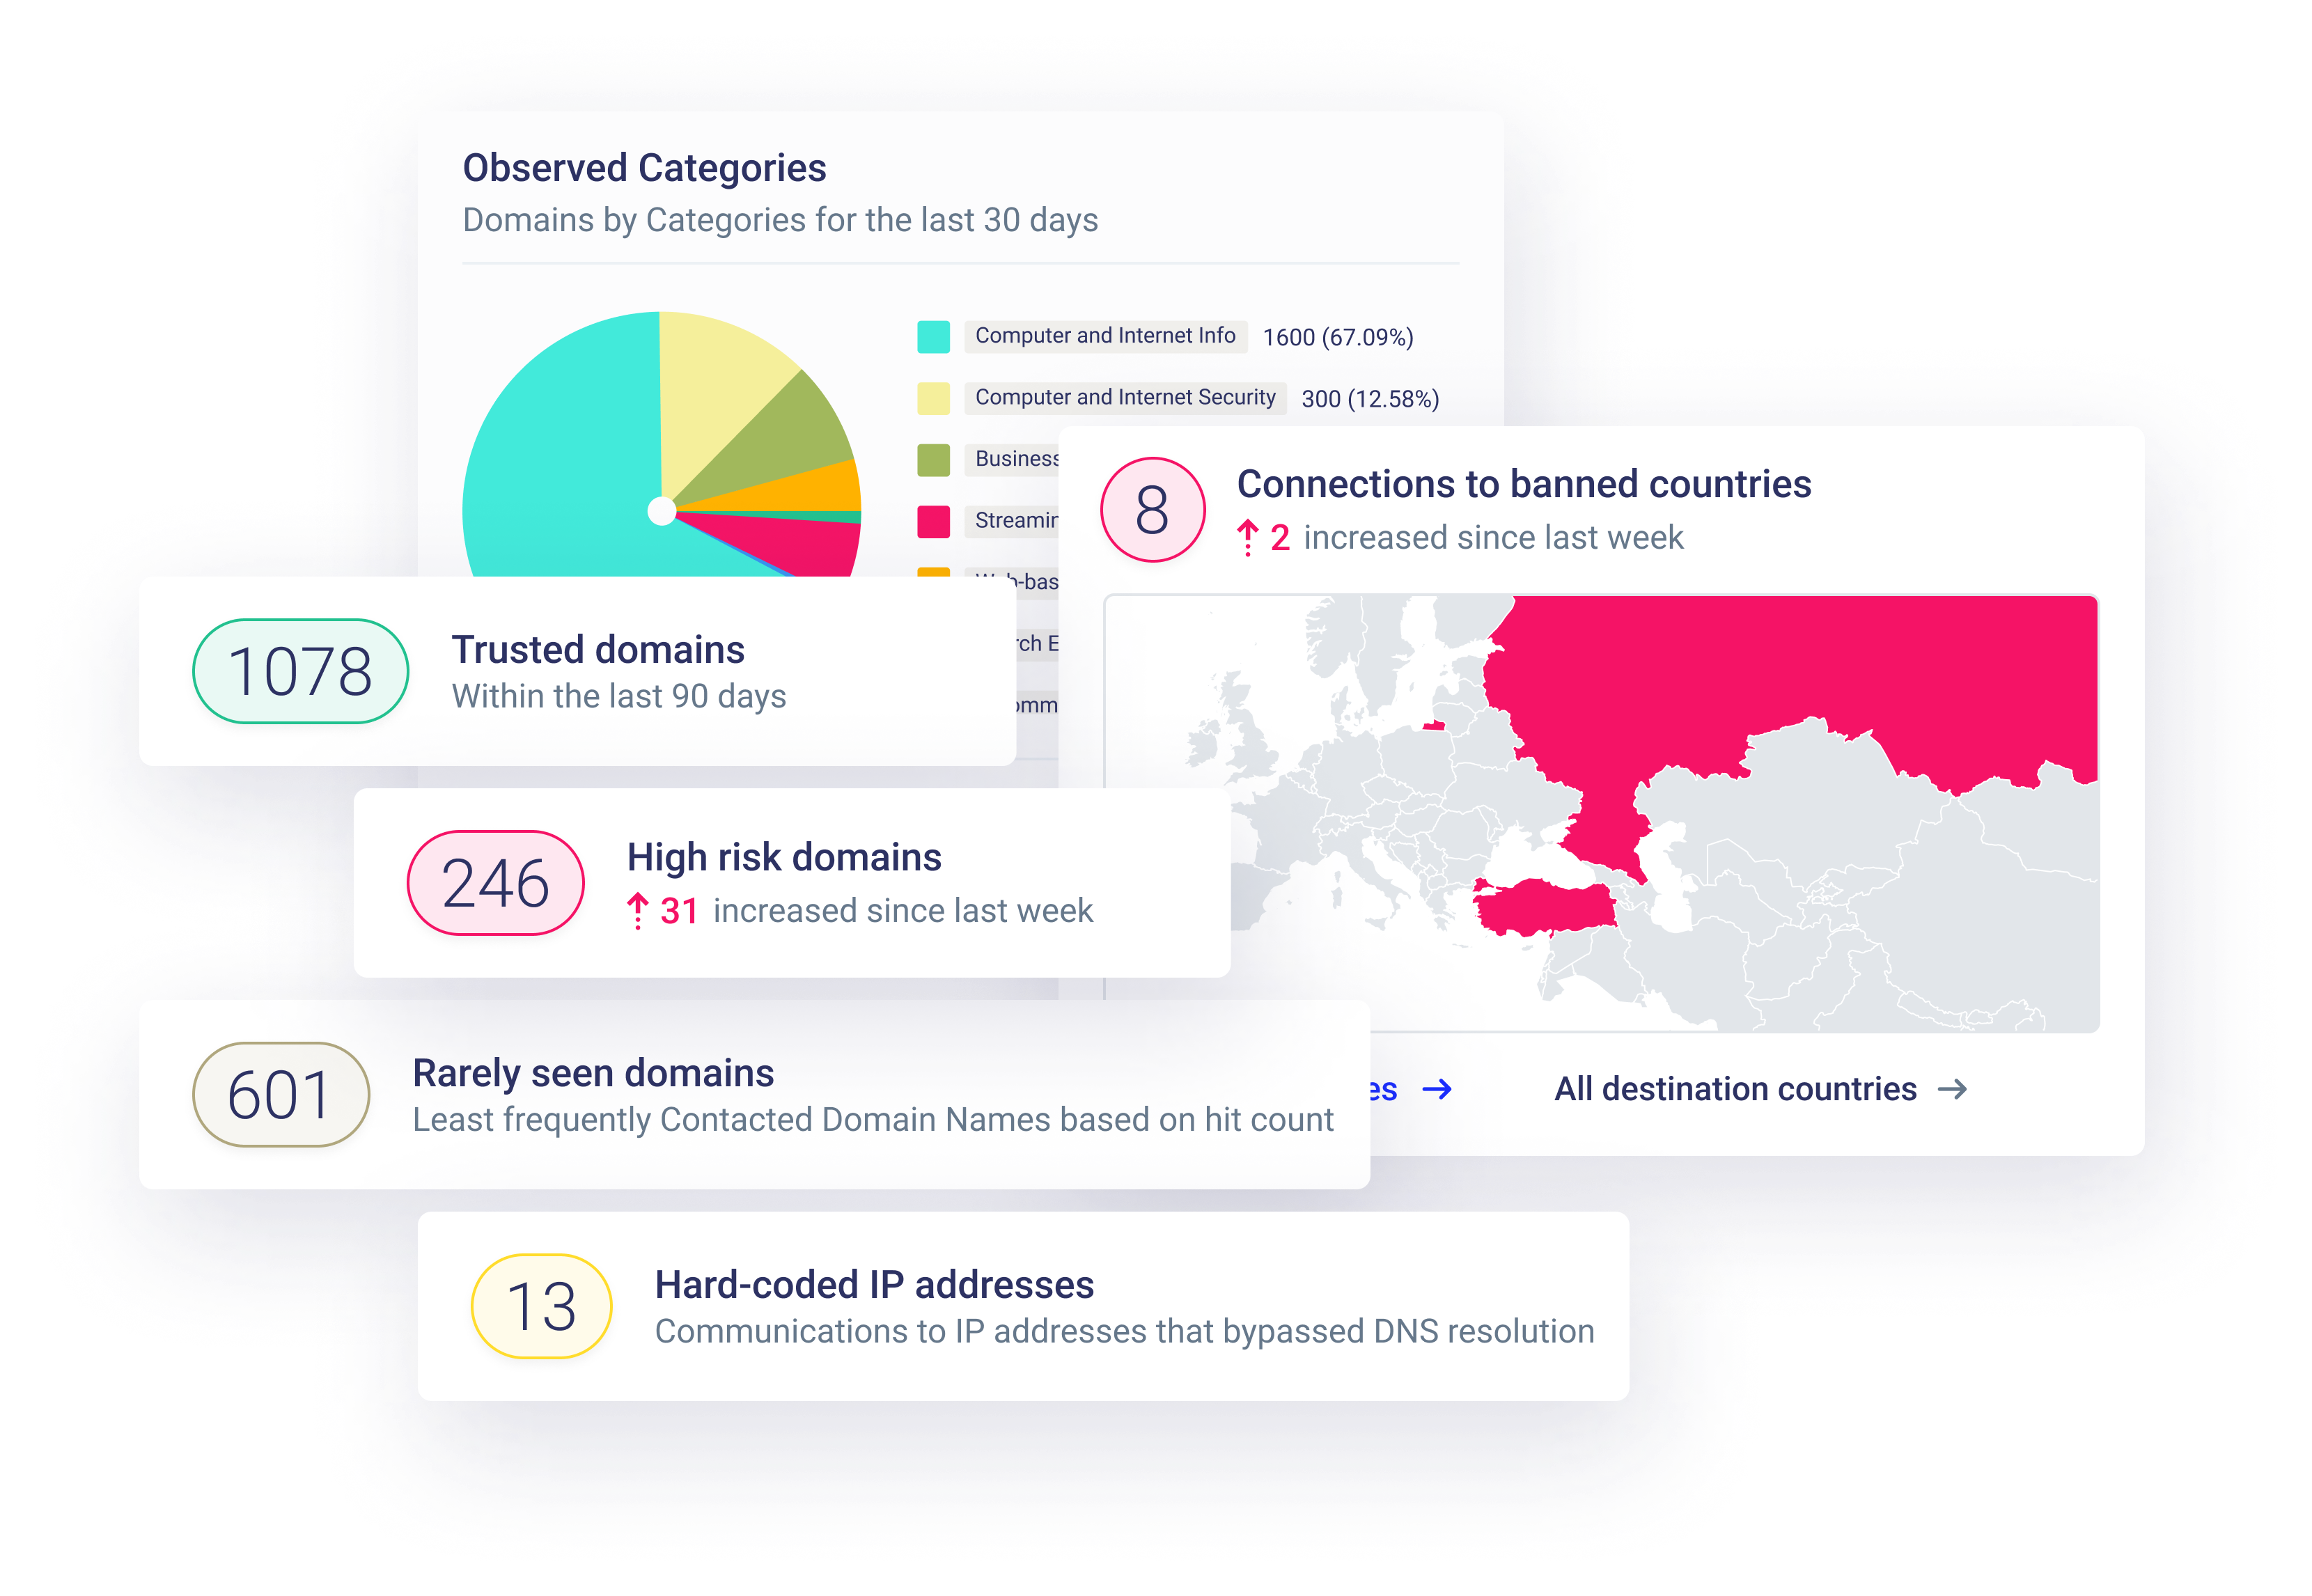
A large AI native healthcare company with a significant cloud footprint across AWS and GCP wanted to understand where its cloud-deployed LLM workloads were communicating. CloudFence surfaced outbound destinations the security team wasn't aware of.
How CloudFence does it
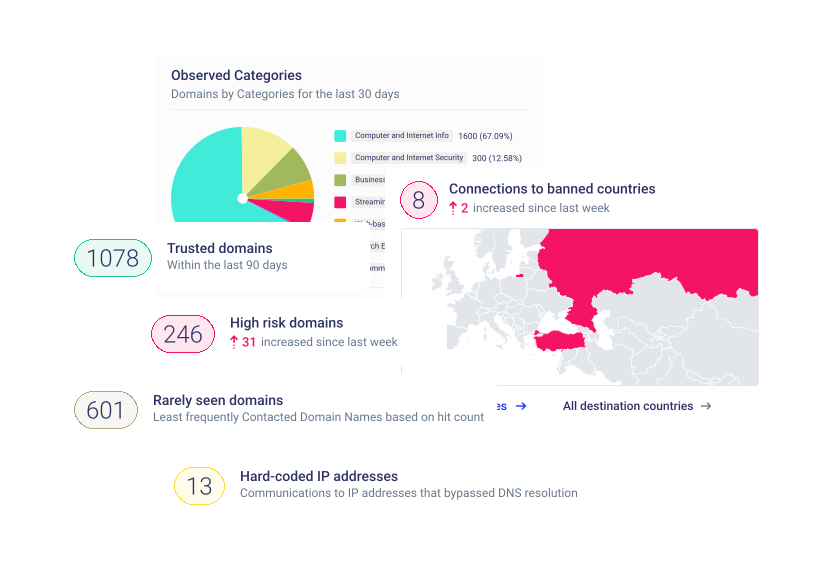
CloudFence continuously analyzes outbound activity across accounts , VPCs and VNETs, classifying destinations by reputation and category, detecting newly contacted destinations, and surfacing communications with high-risk domains or untrusted geographies.
Powered entirely from your native cloud network and DNS logs - no VMs, agents or traffic mirroring required.
Network and Identity Behavioral Deviations
Staging workloads suddenly started communicating with production
While baselining workload communications for an insurance company with ~800 workloads on AWS, CloudFence detected staging workloads unexpectedly communicating with production.
How CloudFence does it
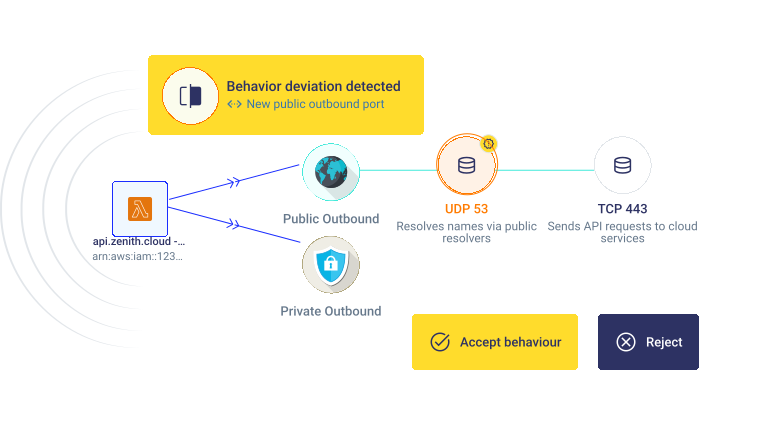
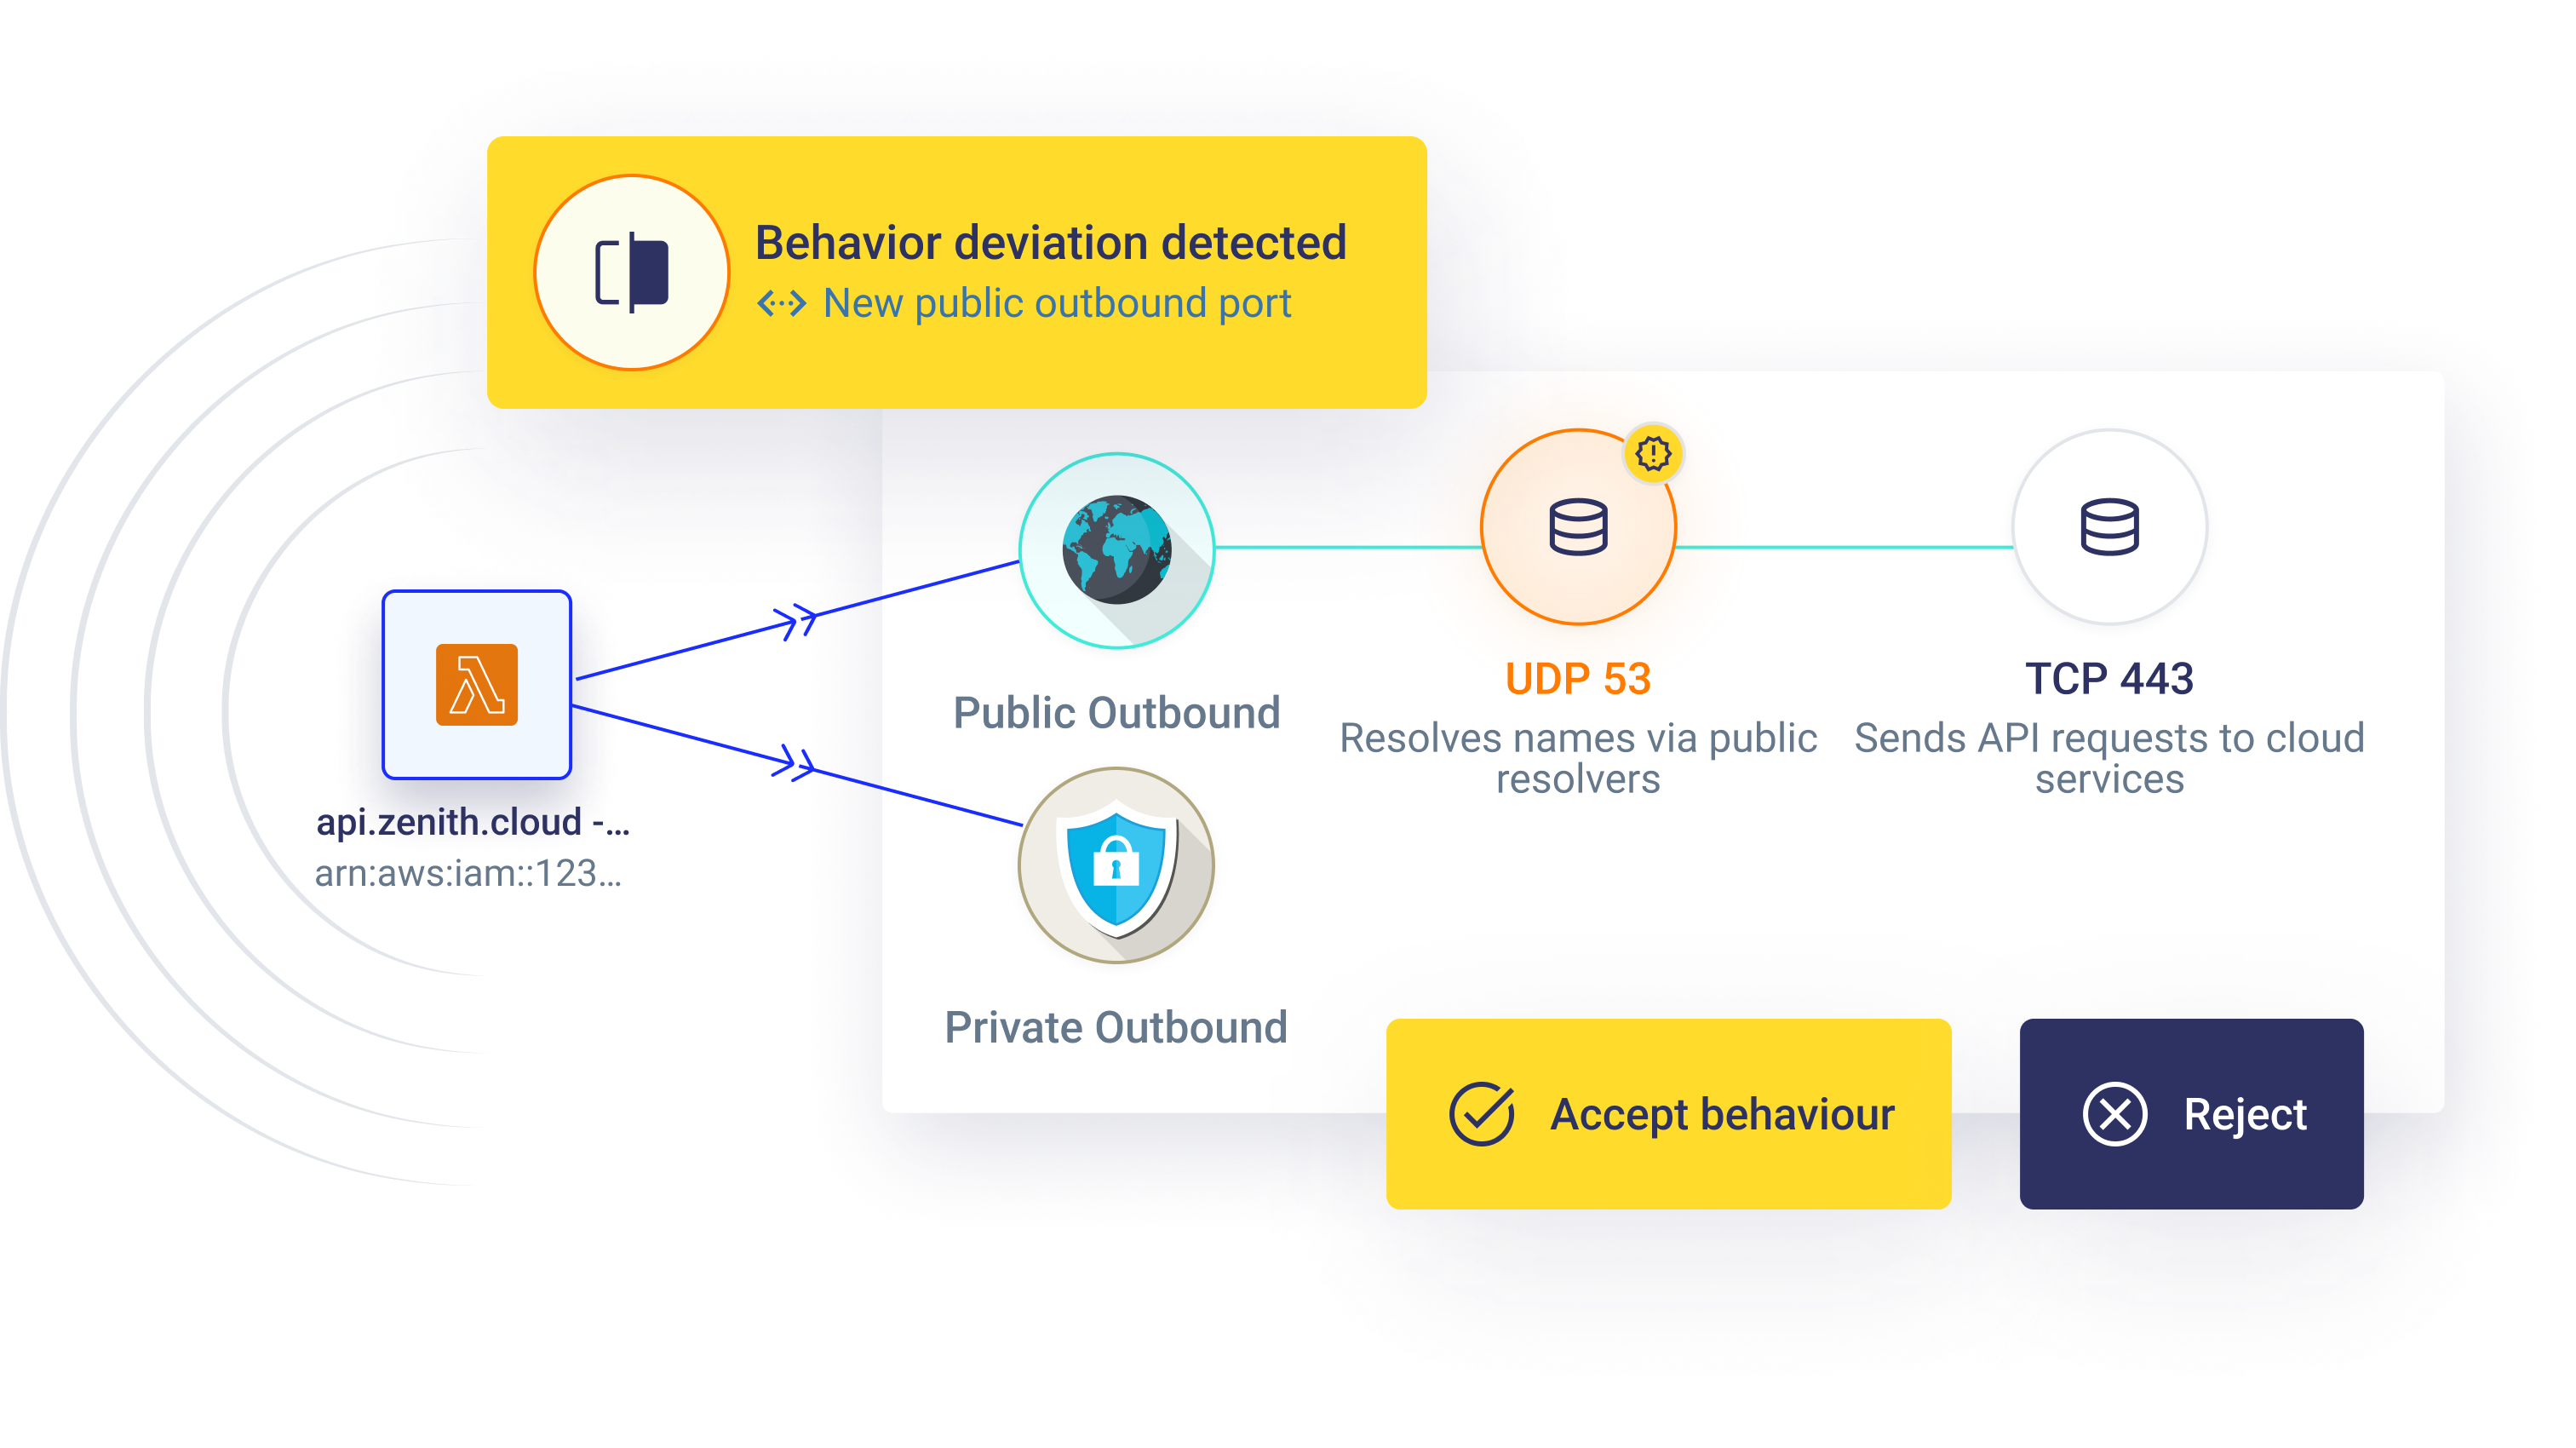
CloudFence continuously analyzes network communications and identities activities across your cloud workloads to build behavior baselines of normal behavior for every asset.
We use native cloud native logs like AWS VPC Flow Logs, CloudTrail, and Azure VNET Flow Logs to understand typical communication patterns, access paths, and privileges over time.
When workloads or identities show anomalous behavior, we flag it instantly, so you can see exactly what unusual activity occurred, how it deviates from normal, and why it's a risk.
Usage-Driven Security Group Cleanup & Least Access
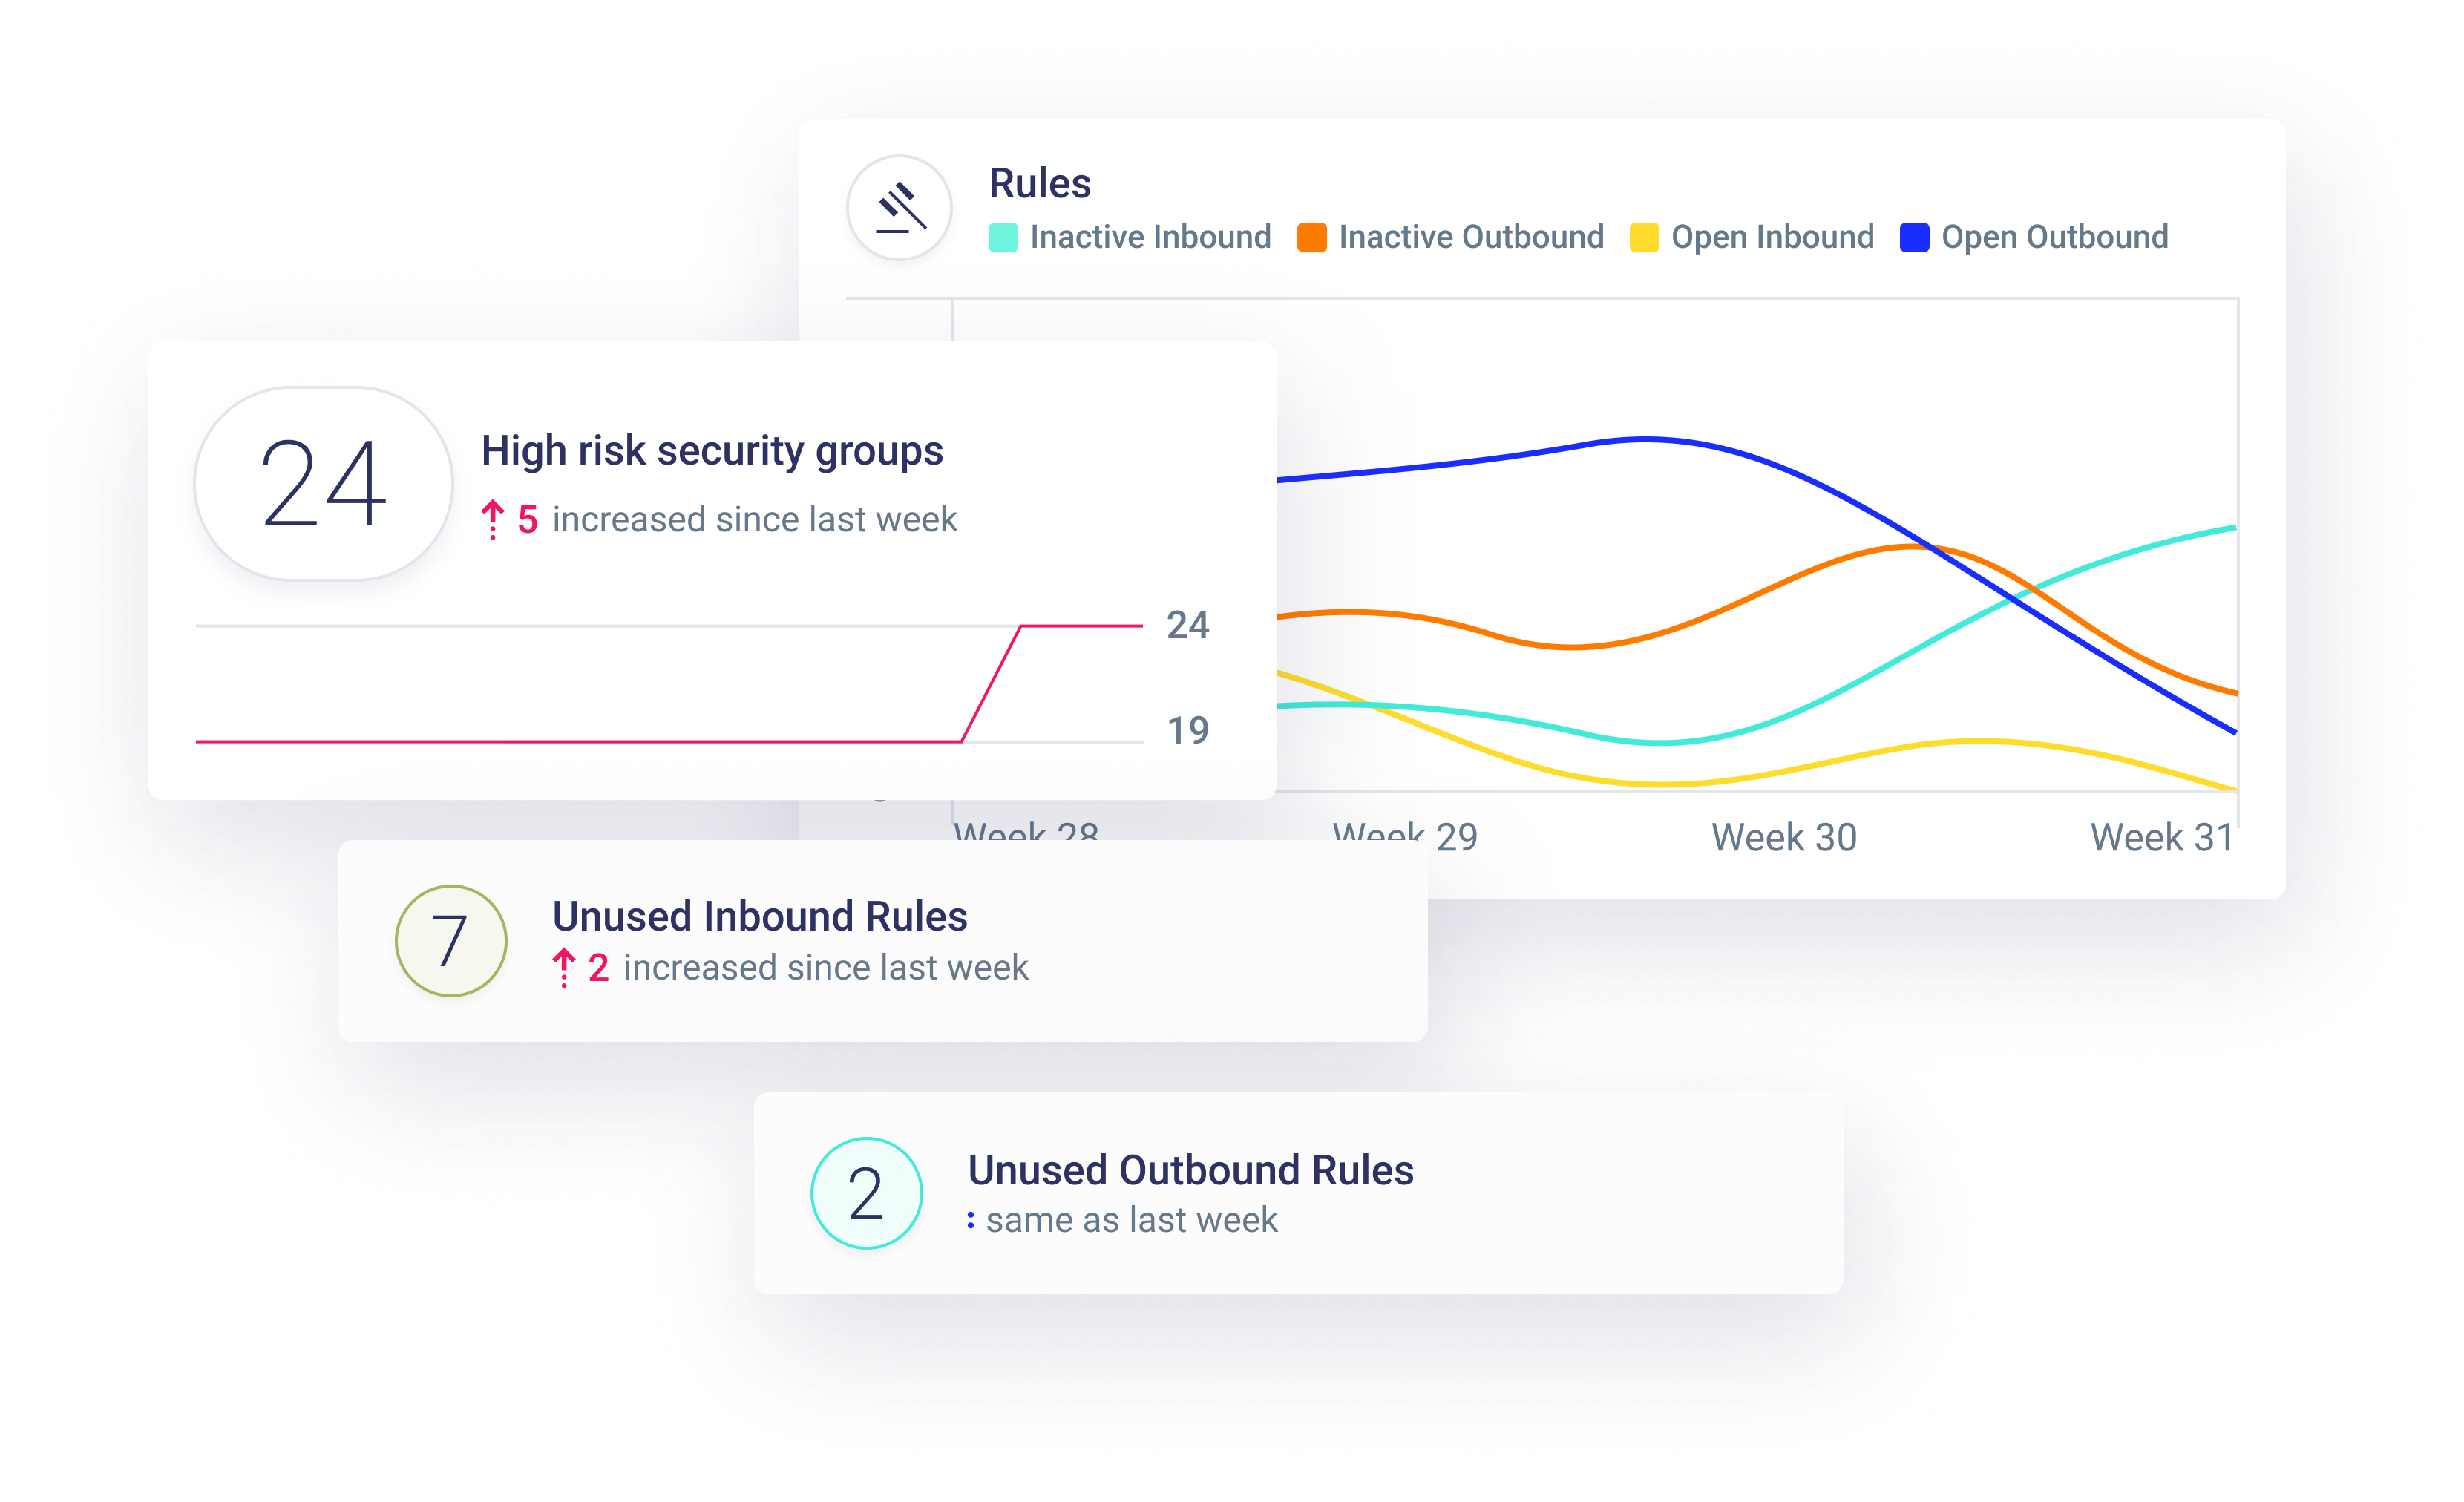
Finding unused access across 8,000+ Security Group rules
A large technology company needed to understand actual usage across more than 8,000 Security Group rules in AWS and remove unused access.CloudFence maps observed communications against the rules allowing them, and gave the DevSecops team the evidence and the confidence to remove unused rules without causing a single production outage.
How CloudFence does it
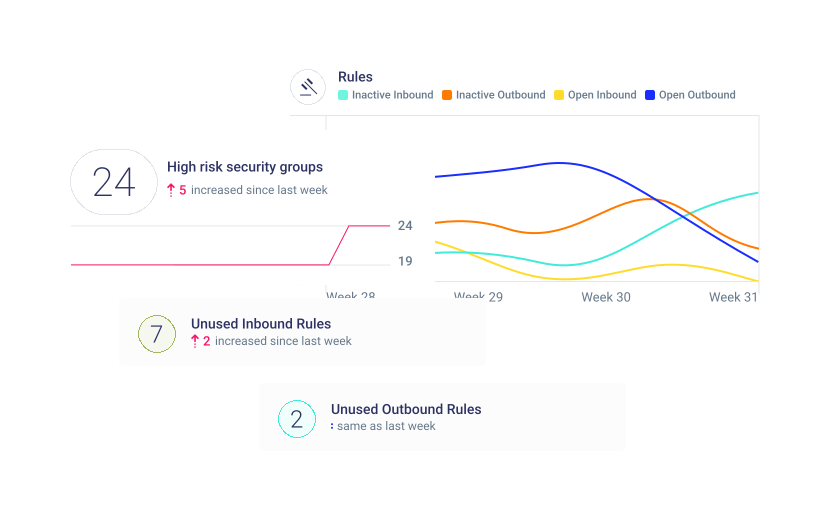
CloudFence continuously analyses cloud network logs and cross-checks every communication to each workload against its security group configuration. It compares configured ports and CIDRs with actual usage to identify unused access and over-permissive rules.
We enrich each security group rule with last active timestamps and hit counts giving teams the confidence to remove or narrow unnecessary access without breaking production.
A workload was bypassing the expected security inspection path
A cybersecurity company running on Azure expected workload traffic to pass through its centralized inspection hub.CloudFence detected a workload connecting directly instead, revealing a communication path the security team wasn't expecting.
How CloudFence does it
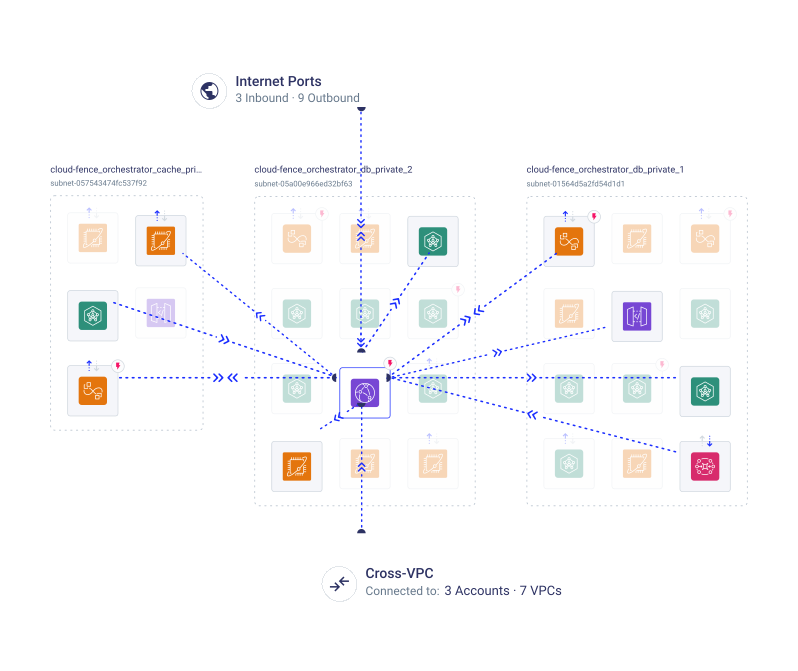
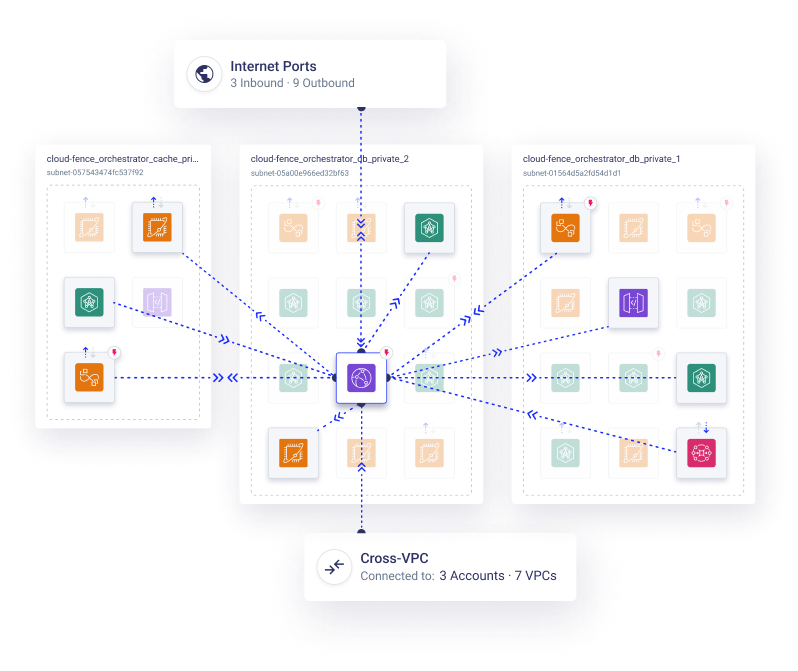
CloudFence combines network logs with cloud infrastructure context to show workload communications and the paths traffic takes through your environment.
Teams can see who communicates with whom, how much data is exchanged, and whether traffic flows through NAT Gateways, VPC Endpoints, Internet Gateways, or other network components, helping Security and DevOps teams verify that traffic follows the intended architecture.